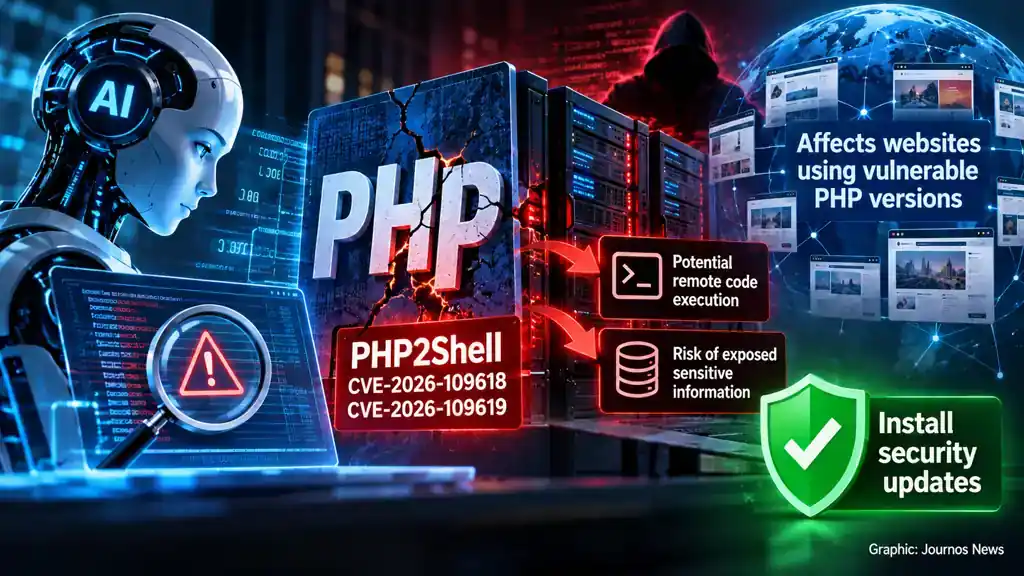
Security researchers have uncovered two critical vulnerabilities in PHP, a programming language used by many websites. Artificial intelligence (AI) helped researchers investigate the flaws and develop ways to exploit them.
The vulnerabilities carry the identifiers CVE-2026-109618 and CVE-2026-109619. Researchers refer to them collectively as PHP2Shell. The flaws could let attackers run code on affected servers without logging in. They could also expose sensitive data, including passwords, authentication tokens and API keys.
PHP released security updates on October 21, 2026, and urged users to install them. The flaws affect PHP itself, not just one website application. As a result, websites built with WordPress, Drupal and Joomla may also face risks if they use affected PHP versions.
The disclosure has prompted software developers, security researchers and technology companies to coordinate their response. Their efforts include releasing fixes, preparing security measures and helping organizations protect systems they cannot update immediately.
How researchers uncovered the flaws
Wiz Research said it used advanced AI models to examine PHP’s memory handling and develop working exploits. Separately, OpenAI reported that Calif found a critical flaw using GPT-5.6 Sol through its Patch the Planet initiative. Wiz said its researchers independently discovered and reported both vulnerabilities.
The flaws involve how PHP handles memory during serious errors, including situations in which a system runs out of memory. Under certain conditions, PHP may leave internal data in an inconsistent state after a request fails. Later requests or processes could then access memory incorrectly.
Researchers demonstrated that the flaws could let attackers run code without authentication on systems using WordPress, Drupal and Joomla. They also demonstrated a separate method for exposing data held in PHP processes.
The PHP security team rated both vulnerabilities as critical and released updates for supported versions.
■ Related News
Wiz said AI helped its researchers turn complex, longstanding weaknesses into practical exploits. The tools also helped them test and refine their methods across different applications and system configurations.
The findings highlight a growing challenge in cybersecurity. AI can help defenders find weaknesses that might otherwise remain hidden. However, attackers could also use similar tools to develop exploits more quickly.
Security updates address the flaws
PHP released patched versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on October 21. The project also advised users of older versions to check with their operating-system distributors or support providers for suitable fixes.
The Canadian Centre for Cyber Security issued an advisory the same day. It warned that internet-facing PHP servers and applications faced increased risk.
The agency advised organizations to identify affected systems, install the appropriate updates and check for signs of compromise.
At the time of its advisory, the agency said it had not identified active exploitation. However, it noted reports that proof-of-concept exploit code was available. That assessment reflected the information available at the time and does not rule out later attacks.
Organizations that cannot patch immediately should consider restricting public access to exposed applications until they can address the vulnerabilities. Security teams should also check web-server, application and authentication logs for suspicious activity.
PHP’s maintainers have stressed that temporary configuration changes do not replace security updates. Installing the appropriate patch remains the main way to address the flaws.
Technology companies coordinate their response
OpenAI said its Patch the Planet initiative brought together software maintainers, researchers and security providers. The participants worked to verify vulnerabilities, develop fixes, test patches and prepare protections before public disclosure.
OpenAI said it worked with PHP maintainers and partners, including Wiz and Cloudflare. Their work covered research, technical support and coordination. OpenAI also described efforts to help infrastructure providers and government cybersecurity agencies distribute guidance.
Wiz separately credited the PHP team, Calif and OpenAI for their roles in discovery, coordination and patch testing. The company also identified technology and infrastructure providers that helped prepare guidance for customers who could not update immediately.
However, releasing a patch does not mean every affected system receives it at once. Software vendors must often incorporate fixes into operating-system packages, hosting platforms and container images. Organizations must then deploy the updated versions across their systems.
What website operators should do
PHP powers many websites and web applications. Because these vulnerabilities affect PHP itself, updating a website’s content-management system alone may not fix the problem. Operators must also check the PHP runtime that the application uses.
Website administrators should first identify the PHP versions running on their servers. They should then install the appropriate security updates and check any services that include their own PHP installations.
Organizations using older PHP versions should ask their vendors whether they provide a backported security fix. If not, they may need to upgrade to a supported version.
The Canadian Centre for Cyber Security also advised organizations to prioritize systems accessible from the internet. Security teams should look for unusual processes, commands, files, accounts and outbound network connections linked to PHP or web-server services.
A suspicious request or publicly available exploit does not, by itself, prove that an attacker breached a website. Administrators should investigate relevant evidence before deciding whether a compromise occurred.
PHP2Shell shows how AI-assisted research can help uncover serious weaknesses in widely used software. The immediate task is to patch affected systems, check for signs of exploitation and reduce the risk of further attacks.
Reporting Credit: PHP Project — Security advisory: Critical remote code execution vulnerabilities, update now. Official disclosure of CVE-2026-109618 and CVE-2026-109619, affected PHP releases, update guidance and temporary risk-reduction measures. Canadian Centre for Cyber Security — Critical vulnerabilities impacting PHP. Government cybersecurity advisory covering risk, fixed versions and recommended defensive measures. OpenAI — Patch the Planet: global response coordination as agents uncover critical vulnerabilities. OpenAI’s account of its work with maintainers, researchers and security providers. This is a primary source for OpenAI’s own activities and claims, not an independent evaluation of its contribution. Wiz Research — PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet. Technical disclosure detailing the vulnerability mechanisms, proof-of-concept demonstrations and researchers’ account of AI’s role.